

HIPAA-aligned design for AFH operations
Access controls, audit trails, encryption, and privacy-respecting workflows - designed for Adult Family Homes that handle sensitive resident and operational information.
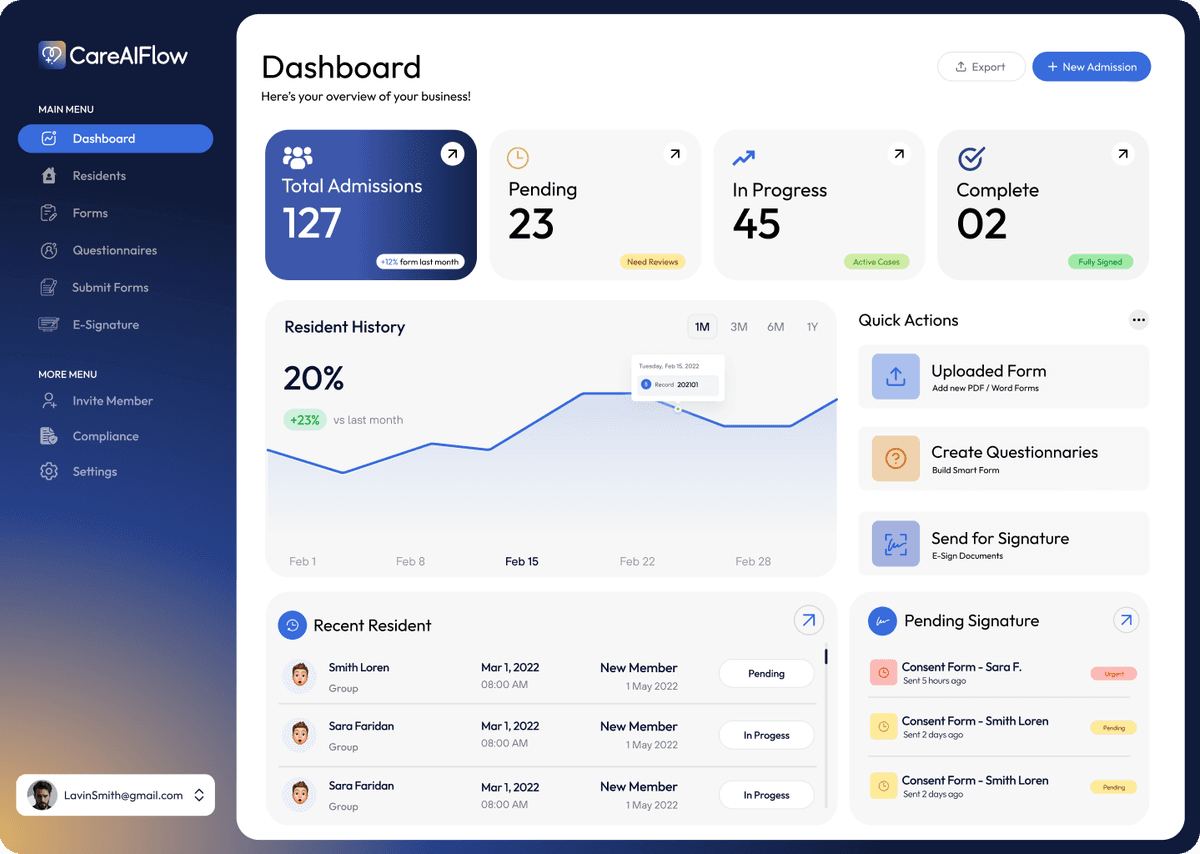
- Access Controls
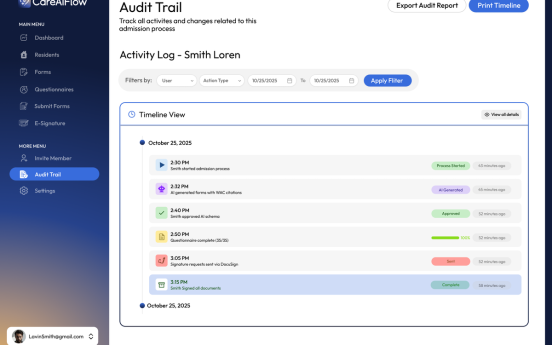
- Audit Trails
- Encrypted Transport
Compliance philosophy
“Opening direction: CareAIFlow was designed by starting with state requirements - not by adding compliance later.”
- Forms must look familiar, data must be traceable, and outputs must be defensible.
Compliance Validation Workflow
System Logic
State Requirements
Platform Design
Documentation
Validation
Inspection Ready
Audit trails and accountability
Supported access and application events help administrators review activity and changes.
Form Traceability
Recorded events support review of supported document and application activity.
User Identity
Supported audit events identify the acting user or system process.
Timestamped Actions
Event timestamps help administrators review activity over time.
Role-Based Permissions
Role and facility permissions restrict access to supported actions.
CareAIFlow
Security architecture
Layered safeguards for healthcare operations.
Application & access
- APIs
- Clinical workflows
- Facility workflows
- Audit reporting
- Sign in
- RBAC & facility checks
- Authorized action
- Recorded audit event
Administrators and authorized staff access these services through sign-in, Role-Based Access Control (RBAC) and facility permissions. Supported actions produce audit events.
Security controls
TLS
Encryption in transit
IAM & MFA
Scoped AWS roles and administrator MFA policy
AWS KMS
Database and server-disk encryption keys
Secrets Manager
Protected application secret storage
Cloud & tenant isolation
Amazon Route 53
DNS
Domain resolution
AWS Amplify
Frontend
Amazon EC2
Application
Server disk: AES-256 at rest
Amazon RDS
Database
AES-256 at rest · KMS-backed keys
Amazon S3
Documents
AES-256 at rest · S3-managed (SSE-S3)
Shared infrastructure · Logical tenant isolation
- Tenant A
- Tenant B
- Tenant C
Database row-level security, facility checks and role permissions
Monitoring & accountability
AWS WAF
Request protection
CloudTrail
AWS activity logging
GuardDuty
Threat detection
CloudWatch
Operational alarms
Audit logs
Supported access and application events
Designed to support customers’ HIPAA obligations. Agreements, policies and risk assessments also matter.

Questions about privacy and security posture?
Talk through access controls, audit trails, and how CareAIFlow handles sensitive AFH operational data - without sales theater.